

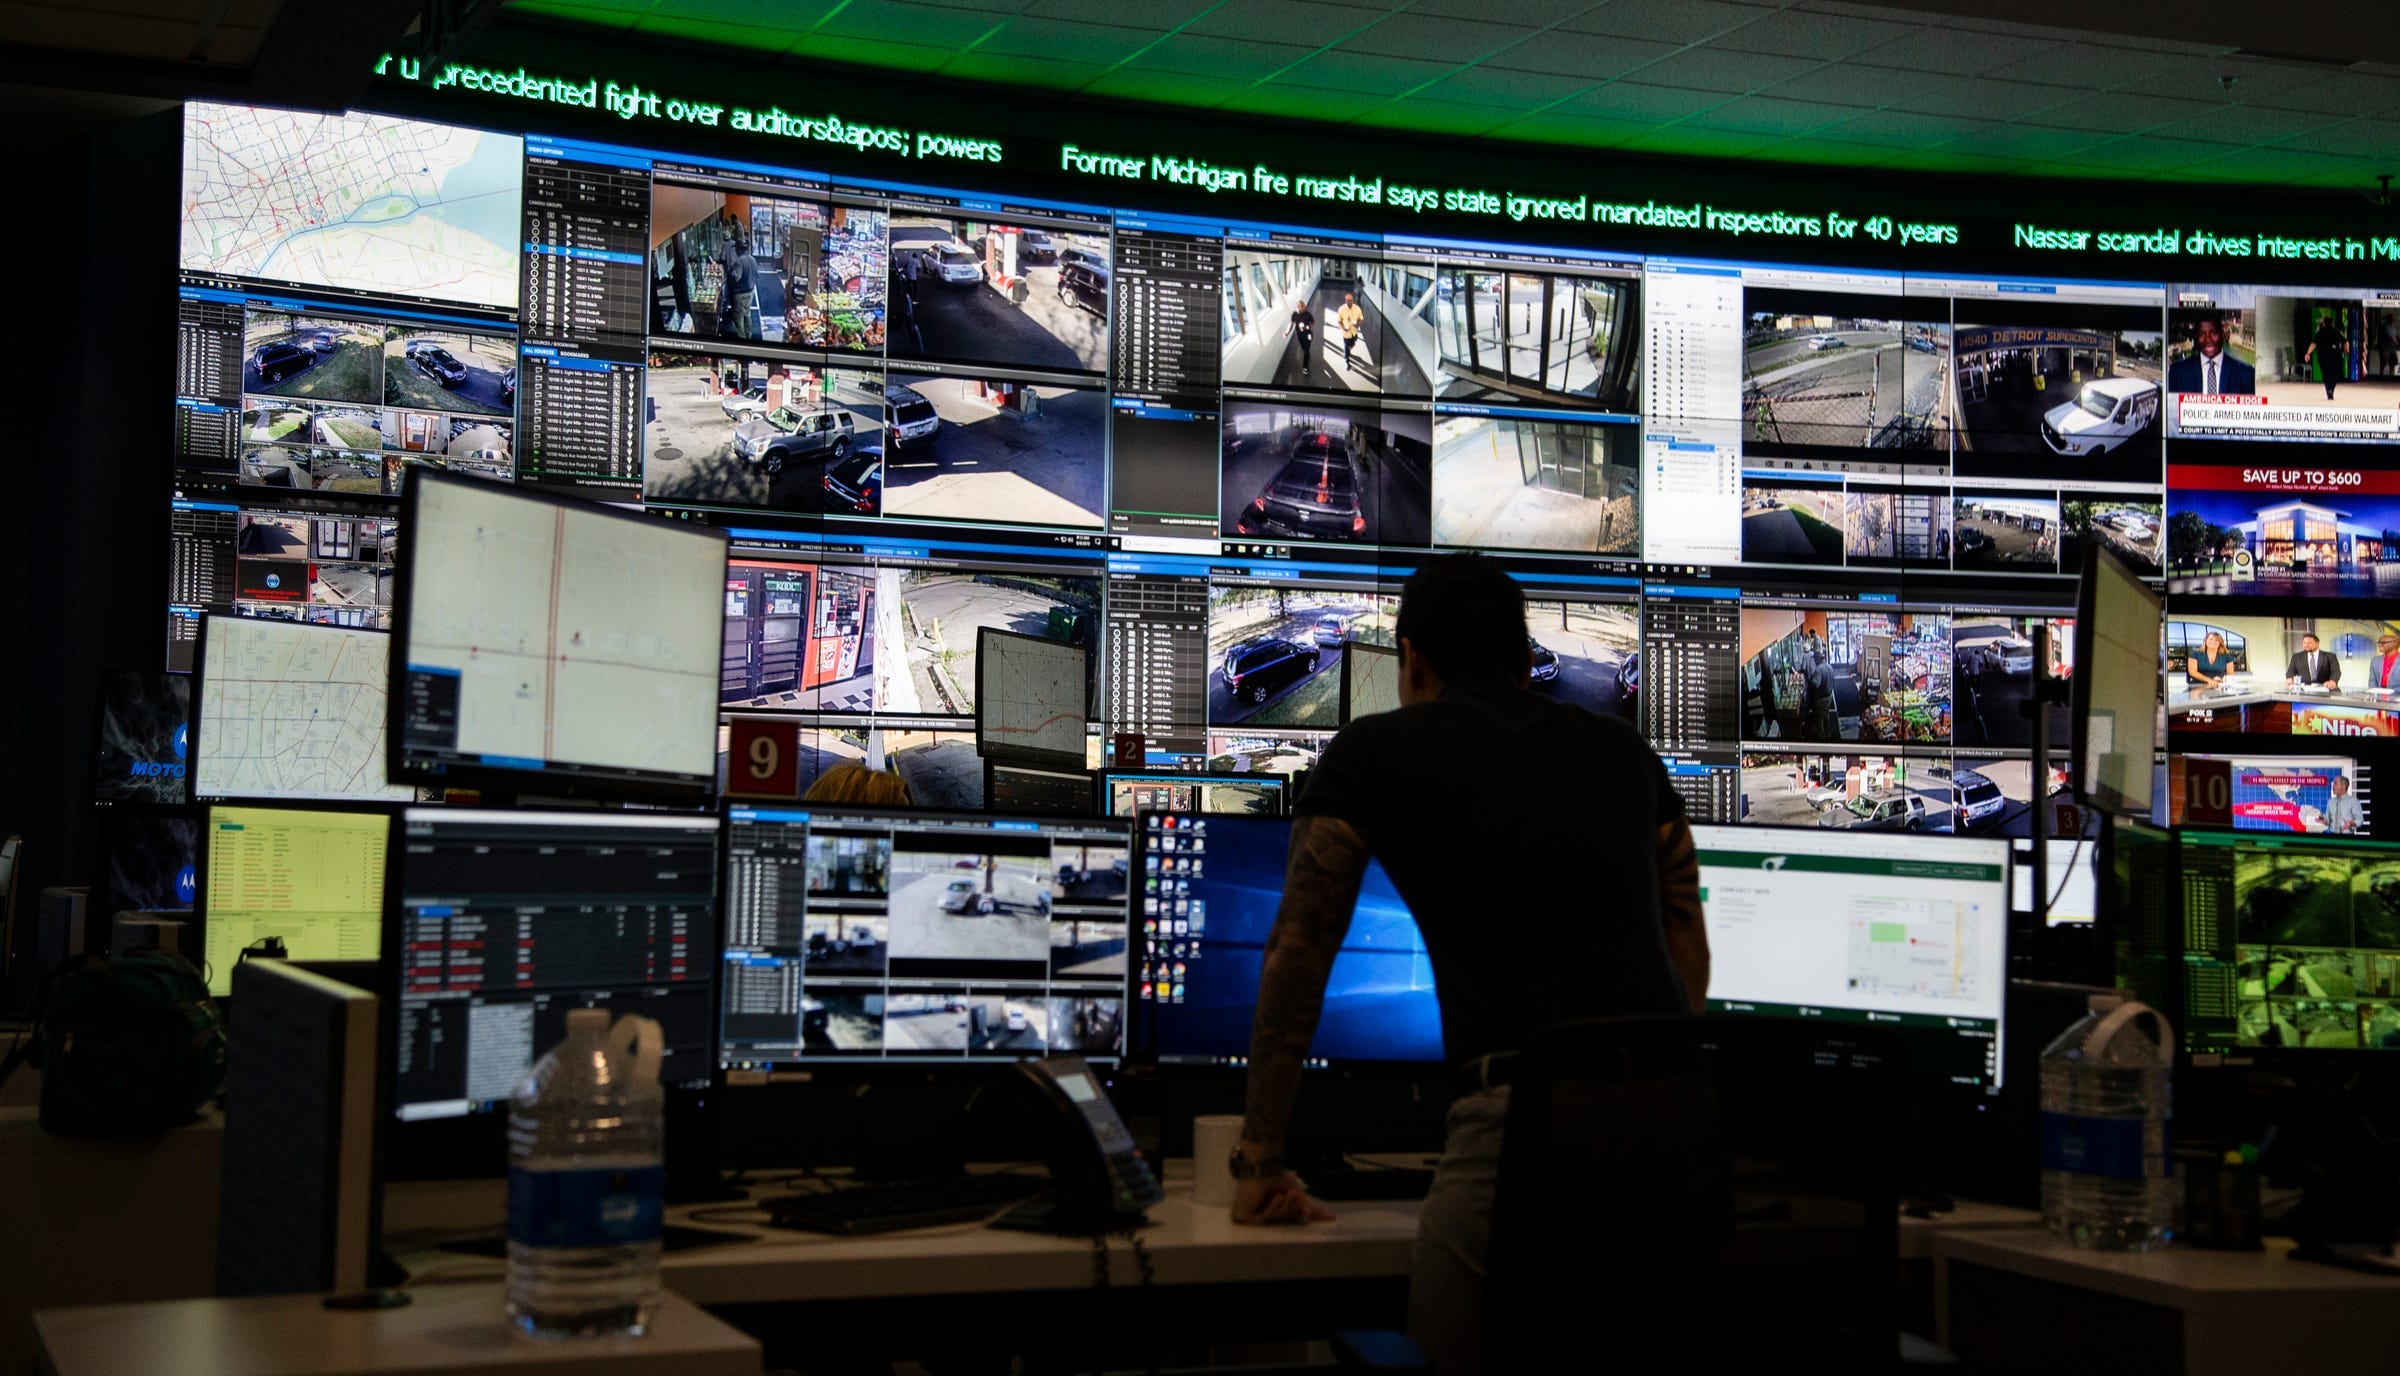
In April 2025, U.S. Immigration and Customs Enforcement paid Palantir Technologies $30 million to build a system called ImmigrationOS. The platform pulls records from the IRS, the Social Security Administration, passport databases, and license plate readers scattered across the country, then fuses them into a single searchable profile of a targeted person. A few months later, the Department of Homeland Security locked in a purchasing agreement with Palantir worth roughly a billion dollars. Since the start of 2025, Palantir alone has been awarded more than $13.7 billion in government contract ceilings, including a $10 billion, ten-year deal with the U.S. Army that folded 75 separate software contracts into one.
None of this required a new law. None of it required a warrant. Most of it did not even require the government to build anything from scratch. It required a purchase order.
That is the story of domestic surveillance in 2026. It is not a single program run out of a single agency. It is an ecosystem, built from two supply chains that have quietly merged into one. The first supply chain is the government’s own surveillance authority, inherited from the Cold War and expanded after September 11. The second is the private data economy, an industry built to track your phone, your face, your car, your DNA, and your browsing habits for advertising purposes, and now repurposed as a vendor to the very government agencies the Fourth Amendment was written to restrain. Where the Constitution blocks the front door, the data broker industry has built a loading dock around back. This investigation walks through both halves of that ecosystem, the legal battles that have tried to slow it down, and the ones still being fought right now.
The Architecture Built After September 11
Modern domestic surveillance law traces back to two Supreme Court cases most Americans have never heard of. In United States v. Miller (1976), the Court ruled that bank records handed over to a bank carry no reasonable expectation of privacy, because the customer voluntarily shared them with a third party. Three years later, in Smith v. Maryland (1979), the Court extended that logic to phone numbers dialed from a home phone, reasoning that a caller assumes the risk that the phone company will disclose that information. Together, these two rulings created what is now called the third party doctrine: once you hand information to a bank, a phone company, or any other outside entity, the government does not need a warrant to obtain it.
For twenty years, the third party doctrine sat mostly dormant. Then came September 11, 2001. The USA PATRIOT Act, passed six weeks later with almost no debate, expanded the government’s authority to collect business records, monitor communications, and share intelligence across agencies. Section 215 of the Patriot Act allowed the FBI to obtain “tangible things,” including phone records, relevant to a terrorism investigation. For years, the public had no idea how broadly the government was interpreting that phrase.
Then, on June 5, 2013, The Guardian published a secret court order compelling Verizon to hand over the phone records of more than 120 million subscribers. Within days, The Washington Post and The Guardian revealed a second program, code-named PRISM, under which the NSA had gained access to the servers of Apple, Facebook, Google, and other major internet companies. The source of both stories was Edward Snowden, a contractor for the NSA who eventually released more than 7,000 classified documents. What those documents showed was not a narrow counterterrorism tool. It was, in the words of journalist Barton Gellman, a global surveillance system that had “cast off many of its historical restraints” after 2001, sweeping in the telephone, internet, and location records of entire populations.
The legal fallout arrived quickly. The ACLU sued in ACLU v. Clapper, arguing that the NSA’s bulk phone metadata program violated the First and Fourth Amendments. A federal judge dismissed the case in December 2013, but the Second Circuit Court of Appeals reversed course in May 2015, ruling that the program exceeded what Congress had actually authorized under Section 215. A parallel case, Klayman v. Obama, produced an even sharper rebuke. U.S. District Judge Richard Leon called the program “almost Orwellian” and issued a preliminary injunction, though the D.C. Circuit later vacated it on standing grounds rather than reaching the merits. Congress responded in June 2015 by passing the USA Freedom Act, which ended the bulk collection of American phone records and required the NSA to request specific records from phone companies rather than vacuuming up everything at once. The bulk program was formally shut down that November.
That was, for a moment, treated as a victory. It was also a narrow one. The USA Freedom Act reformed one program. It left the broader surveillance architecture, and the legal doctrines underneath it, almost entirely intact.
FISA Section 702: The Program That Would Not Die
Section 702 of the Foreign Intelligence Surveillance Act authorizes the government to collect communications of foreigners located outside the United States without an individual warrant. In practice, because Americans routinely communicate with people overseas, this sweeps in enormous volumes of communications involving U.S. citizens, which the FBI can then search using an American’s name, email address, or phone number. Privacy advocates call these searches “backdoor searches,” because they let the FBI query a database of communications collected without a warrant using the identifiers of the very people the Fourth Amendment is supposed to protect.
Section 702 was set to expire in April 2024. After a bruising fight in Congress, lawmakers passed the Reforming Intelligence and Securing America Act, which reauthorized the program for two years and imposed new limits on U.S. person queries, including a ban on searches “solely designed to find and extract evidence of criminal activity.” An amendment that would have required a warrant before querying an American’s communications failed in the House by a handful of votes.
The new limits did not hold. In August 2024, Justice Department overseers discovered that the FBI had been quietly using a query tool that let analysts bypass the very safeguards RISAA had just imposed, including the requirement to get supervisory or attorney approval before running a backdoor search. The FBI said it fixed the problem in early 2025. In March 2026, the Foreign Intelligence Surveillance Court found that the underlying issue was still happening, and that it extended beyond the FBI to other parts of the intelligence community.
Section 702 lapsed on schedule in mid-2026 while Congress argued over how to fix it. Lawmakers passed a 45-day clean extension at the end of April to buy time for negotiations, and as of this writing, the debate over a longer-term reauthorization, and whether to finally require a warrant for U.S. person queries, remains unresolved. Representative Andy Biggs has introduced the Protect Liberty and End Warrantless Surveillance Act, which would impose exactly that warrant requirement and also restrict federal agencies from buying personal data from commercial brokers without legal authorization. The bill’s existence is itself telling. More than a decade after Snowden, Congress is still trying to pass a law establishing that the government cannot read an American’s messages without a judge’s approval.
The Marketplace Loophole: Buying What the Constitution Says You Cannot Seize
Carpenter v. United States, decided by the Supreme Court in 2018, was supposed to close the gap the third party doctrine had opened. Timothy Carpenter’s cell phone provider handed over 127 days of his location history to police, obtained through a court order that required a lower standard than probable cause. Chief Justice John Roberts, writing for a 5-4 majority, ruled that the government could not obtain “the whole of a person’s physical movements” without a warrant, comparing continuous cell-site tracking to “attaching an ankle monitor” to someone’s phone. It was the first time the Court had meaningfully limited the third party doctrine in the digital age.
Roberts also wrote a narrow opinion. He explicitly declined to overturn the third party doctrine itself, and he limited the ruling to historical cell-site records specifically, leaving open how the same logic might apply to other kinds of purchased or aggregated data. Federal agencies found the opening almost immediately.
If a warrant is required to compel a phone company to hand over location data, agencies reasoned, then simply buy the same data from a company that already collected it for advertising purposes. The Electronic Communications Privacy Act bars phone and internet carriers from selling sensitive customer data directly to the government, but it says nothing about data brokers, the industry of middlemen that buys location and behavioral data from mobile apps, aggregates it, and resells it to whoever will pay. Companies like Venntel and Babel Street built businesses on exactly that gap, and agencies including DHS, ICE, the FBI, the IRS, and the Secret Service have all purchased location, browsing, and personal data through them.
The scale of the resulting industry is enormous. Acxiom, now part of Omnicom’s Real ID identity platform, maintains profiles tied to roughly 2.6 billion verified global identities. LexisNexis and the background-check platform CLEAR, combined with Palantir’s data-fusion software, give ICE’s Enforcement and Removal Operations division the ability to build detailed surveillance profiles on immigration targets. A single Thomson Reuters contract, worth $22.8 million, gave ICE access to CLEAR’s license plate reader data. In March 2026, roughly 200 Thomson Reuters employees signed a letter demanding the company decline to renew that ICE contract when it expired at the end of May. Palantir, meanwhile, has taken in over $180 million from the IRS since 2018 across 26 contracts, a relationship now under scrutiny amid concerns about how taxpayer data is being used and shared.
Congress has tried, and so far failed, to close this loophole legislatively. The Fourth Amendment Is Not For Sale Act, which would ban federal agencies from buying data they would otherwise need a warrant to obtain, passed the House in April 2024 with bipartisan support. It never received a Senate vote before that Congress ended, meaning it would need to be reintroduced and pass again from scratch. As of this writing, the government’s authority to simply purchase what it cannot lawfully seize remains fully intact, and the volume of contracts built on that authority keeps growing.
The Local Surveillance Web: Cameras, Plates, and Doorbells
Federal agencies are not the only ones building this ecosystem. Local police departments have assembled a parallel surveillance layer built on cameras, and 2026 has become the year that layer started facing serious legal resistance.
Automated license plate readers, deployed on patrol cars and fixed poles across thousands of cities, photograph every passing vehicle and log its plate, time, and location into a searchable database. Flock Safety has become the dominant vendor in this space, and its centralized network is now the subject of a rapidly expanding wave of litigation. A class action filed in San Francisco Superior Court in February 2026, later amended in April, alleges that Flock let out-of-state and federal law enforcement agencies search San Francisco’s plate database more than 1.6 million times in seven months, in direct violation of a California law that bars local police from sharing that data across state or federal lines. Within six weeks of a landmark February appellate ruling, at least four more class actions were filed against malls, medical centers, and commercial campuses that deployed Flock cameras without complying with state privacy law, and at least eight additional investigations are actively recruiting plaintiffs. Some cities have simply pulled out. Santa Cruz voted to end its Flock contract in January 2026, and Mountain View’s police chief announced the department would immediately stop using the cameras the following month.
Amazon’s Ring has run its own version of this story. In 2025, Ring rolled out a “Community Requests” feature letting roughly 5,000 police agencies request doorbell footage directly through Flock Safety’s platform, replacing an earlier program the company had shut down in 2024 after public criticism. The backlash to the new arrangement was immediate, and it intensified sharply after a Ring Super Bowl ad promoted a feature called “Search Party” that critics described as blanketing entire communities with AI-driven surveillance. In February 2026, Amazon canceled the Flock partnership outright. It kept a separate arrangement with Axon that still allows police to request footage from Ring users, meaning the retreat was partial, not complete.
Facial recognition has followed its own long and unresolved legal arc. Clearview AI built a database of more than 60 billion facial images by scraping photos from social media, news sites, and other public corners of the internet, then sold access to law enforcement and private clients. Eleven separate lawsuits alleging violations of state biometric privacy laws, including Illinois’s Biometric Information Privacy Act, were consolidated into multidistrict litigation. In March 2025, a federal judge approved a novel settlement granting the plaintiff class a 23 percent equity stake in Clearview, valued at roughly $51.75 million, rather than a cash payout the company could not afford. That settlement did not hold. The Seventh Circuit Court of Appeals vacated it in July 2026, finding procedural problems in how the lower court approved the deal, and sent the case back down. More than five years after the first lawsuits were filed, one of the most consequential biometric privacy cases in the country is still unresolved.
Your Body Is Data Too: Genetic and Biometric Surveillance
License plates and faces are only part of the picture. Genetic information has become searchable in ways most people who submitted a DNA sample never anticipated. GEDmatch, a genealogy platform originally built to help people find relatives, updated its terms in 2018 to allow law enforcement to search its database while investigating violent crimes, and it now requires every user to affirmatively opt in or out of that access. The opt-out has proven porous. Forensic genetic genealogists have been documented working around users’ opt-out choices, and a 2020 security breach temporarily reset every user’s privacy settings without their knowledge, exposing opted-out profiles to search for roughly three hours before the issue was caught. A single DNA sample uploaded for a genealogy hobby can now, indirectly, implicate relatives who never used the service and never consented to anything.
This is the same underlying dynamic that runs through the rest of the surveillance ecosystem: data collected for one purpose, under one set of assumptions, becomes searchable for an entirely different purpose once it exists. It is true of a phone’s location history, a doorbell camera’s footage, and a genealogy database’s DNA matches alike.
The Automation of Suspicion
Police departments have also started outsourcing the question of who to watch to algorithms. Predictive policing software takes historical crime data and generates forecasts about where crime is likely to occur or who is likely to be involved. In practice, because that historical data reflects decades of policing patterns already skewed toward over-policed neighborhoods, the algorithms tend to reproduce and amplify those same patterns rather than correct them.
The legal reckoning has already claimed some of the most prominent programs. The Los Angeles Police Department discontinued its use of PredPol in 2021 after years of criticism over low accuracy and racial bias. Chicago decommissioned its “Strategic Subject List,” which scored people on their likelihood of being involved in future shootings, in 2020. In Florida, four residents sued the Pasco County Sheriff’s Office over its intelligence-led policing program, and the office ultimately settled the case by admitting it had violated residents’ constitutional rights to privacy and equal treatment under the law. The technology is not slowing down even as individual programs fall. The Justice Department’s most recent AI use case inventory logged 315 separate applications across the department in 2025, a 31 percent jump from the year before, spanning everything from litigation support to public surveillance to crime prediction.
The Border Exception
At the nation’s borders, the Fourth Amendment operates under its own separate, weaker set of rules. Courts have long recognized a “border search exception” that allows agents to search belongings without a warrant or individualized suspicion, a doctrine built for suitcases and shipping containers long before it was ever applied to a smartphone carrying years of someone’s messages, photos, and financial records.
Customs and Border Protection now distinguishes between a “basic search,” which requires no suspicion at all, and an “advanced search,” where agents connect external equipment to copy and analyze a device’s contents, which requires reasonable suspicion. In fiscal year 2025, CBP conducted 55,318 searches of electronic devices at the border, more than 13,500 of them involving U.S. citizens. One of those citizens, Wilmer Chavarria, was detained for more than four hours at a Houston airport in July 2025 before agents told him he had no Fourth Amendment right to refuse a search of his phone, tablet, and laptop, and released him only after he handed the devices over. The Pacific Legal Foundation has since sued DHS on his behalf, arguing that a phone’s contents are exactly the kind of “papers and effects” the Fourth Amendment was written to protect, and that the border exception was never meant to reach a device holding a person’s entire digital life. The Electronic Frontier Foundation has separately urged both the Third and Fourth Circuit Courts of Appeals in 2026 to rule that these searches require a warrant. Those cases remain pending.
Private Surveillance Capitalism: The Ecosystem Feeding the State
None of the government’s purchased surveillance would exist without a private industry built to harvest data in the first place. That industry runs primarily on advertising, and its legal troubles in 2025 alone illustrate how far the collection has outpaced any meaningful consent.
A jury verdict delivered in September 2025 found that Google had continued collecting personal data from nearly 100 million users even after they explicitly disabled tracking through the company’s “Web & App Activity” setting, doing so for eight years through partnerships with popular apps including Uber, Venmo, and Instagram. Meta has faced its own wave of litigation over the Meta Pixel, a tracking snippet embedded across thousands of third-party websites, with class actions alleging the code intercepts user data in violation of state wiretapping laws and the federal Video Privacy Protection Act. A separate complaint filed in June 2025 accused Meta of exploiting Android vulnerabilities, in cooperation with the Russian firm Yandex, to let Facebook and Instagram bypass a phone’s privacy protections and collect data covertly between September 2024 and June 2025. And in July 2025, Meta executives were named in an $8 billion lawsuit alleging systematic violations of an existing FTC privacy order.
The commercial spyware industry has produced an even more direct collision with the courts. NSO Group, the Israeli company behind the Pegasus spyware, used WhatsApp’s own servers to install its surveillance tool on more than 1,400 devices, prompting Meta and WhatsApp to sue in 2019. In December 2024, a federal judge granted summary judgment against NSO Group on every claim, finding it liable for violating both the Computer Fraud and Abuse Act and California’s computer data access law. A jury followed in May 2025 with a unanimous verdict awarding $167 million in punitive damages, the first jury verdict ever returned against a commercial spyware company in a U.S. court. A judge later reduced that award to roughly $4 million while keeping in place a permanent order barring NSO from ever targeting WhatsApp again. The case took six years from filing to final judgment, a timeline that illustrates how slowly the legal system moves relative to how fast surveillance technology spreads.
The Federal Trade Commission has had some success reining in the location-data side of this industry specifically. In January 2024, the FTC finalized an order banning the data broker X-Mode Social and its successor Outlogic from selling sensitive location data after finding the company had no policy, until May 2023, to strip data tied to medical clinics, places of worship, or protest locations before selling it. In May 2026, the FTC reached a similar order against Kochava, another major location broker, banning it from selling sensitive location data without a consumer’s affirmative, specific consent. These are real wins. They are also narrow ones, targeting individual companies one enforcement action at a time, while the broader data broker industry that supplies the government continues operating largely unregulated at the federal level.
The Legal Battlefield and the Patchwork Left Behind
Step back from any single program, and the shape of the wider legal fight becomes clear. The Supreme Court has repeatedly signaled, in United States v. Jones in 2012 and again in Carpenter in 2018, that the aggregation of surveillance data over time raises constitutional concerns that a single data point does not. Justice Sonia Sotomayor’s concurrence in Jones argued that tracking someone’s movements for even a single day might be permissible while tracking them for a month reveals a portrait of their entire life. That principle has never been extended into a comprehensive rule. Lower courts remain split on how far it reaches. Congress has not codified it. The result is a body of law that recognizes the danger of aggregated surveillance in theory while doing almost nothing to stop its accumulation in practice.
Into that vacuum, states have stepped in unevenly. Twenty states had comprehensive data privacy laws in effect at the start of 2026, and that number had grown to roughly two dozen by midyear as Indiana, Kentucky, and Rhode Island brought new statutes online. Eight states, including Colorado, Connecticut, Texas, and Virginia, amended their existing privacy laws in 2025 alone. That leaves more than half the country with no comprehensive data privacy statute at all, and even the states with laws on the books rarely restrict what government agencies themselves may purchase or collect. No comprehensive federal privacy law exists. The Fourth Amendment Is Not For Sale Act sits unpassed. The Protect Liberty and End Warrantless Surveillance Act sits unpassed. FISA Section 702 sits in a state of repeated short-term extension while its own oversight court documents ongoing noncompliance with the rules Congress wrote just two years ago.
Conclusion: A System Designed to Never Ask Permission
Look across every piece of this investigation and a single pattern repeats. A legal rule draws a line. A technology or a business model appears on the other side of that line. An agency buys, borrows, or partners its way across, and the line stops functioning as a boundary at all. The third party doctrine created the opening. Data brokers turned the opening into an industry. Palantir, LexisNexis, Flock Safety, Clearview AI, and dozens of smaller vendors built the pipes connecting that industry directly into federal, state, and local law enforcement. Section 702 supplies the foreign intelligence justification for scooping up American communications. The border exception supplies the justification for searching an American’s phone without any suspicion at all. Each piece has its own legal rationale. Assembled together, they form something closer to a general surveillance capability than the specific, narrow authorities Congress and the courts have actually approved.
The legal battles chronicled here, Carpenter, Jones, ACLU v. Clapper, the Clearview settlement now back in litigation, the Flock class actions working through California courts, the NSO Group verdict, the border search cases pending before two circuit courts, are not separate stories. They are the same fight, waged in a dozen courtrooms at once, over whether the Fourth Amendment still means what it says once the government can simply purchase, partner, or automate its way around a warrant requirement. Some of those fights have been won. The USA Freedom Act ended bulk phone metadata collection. The FTC forced X-Mode and Kochava out of the sensitive location data business. A jury held a spyware company liable for the first time in American legal history. Others remain wide open, and the government’s purchasing power in this space keeps growing faster than the litigation can catch up to it.
None of this requires believing in a conspiracy. It requires only reading the contracts, the court filings, and the settlement terms already sitting in the public record. The men who wrote the Fourth Amendment could not have imagined a data broker or a facial recognition database, but they understood the underlying danger precisely: that a government left unchecked will use every tool available to watch its own people, and that the only durable check on that impulse is a legal line the government cannot buy, partner, or automate its way across. Right now, in 2026, that line exists mostly on paper. Rebuilding it in practice is the work still ahead.
Margin of the Law publishes constitutional analysis, civic research, and legal education for people who want to understand the system they actually live in. Read the Full Constitutional Analysis Library at marginofthelaw.com.
© 2026 – MK3 Law Group
For republication or citation, please credit this article with link attribution to marginofthelaw.com.